merged
njain006/costly-oss • 5:59 PM - Sep 16, 2026
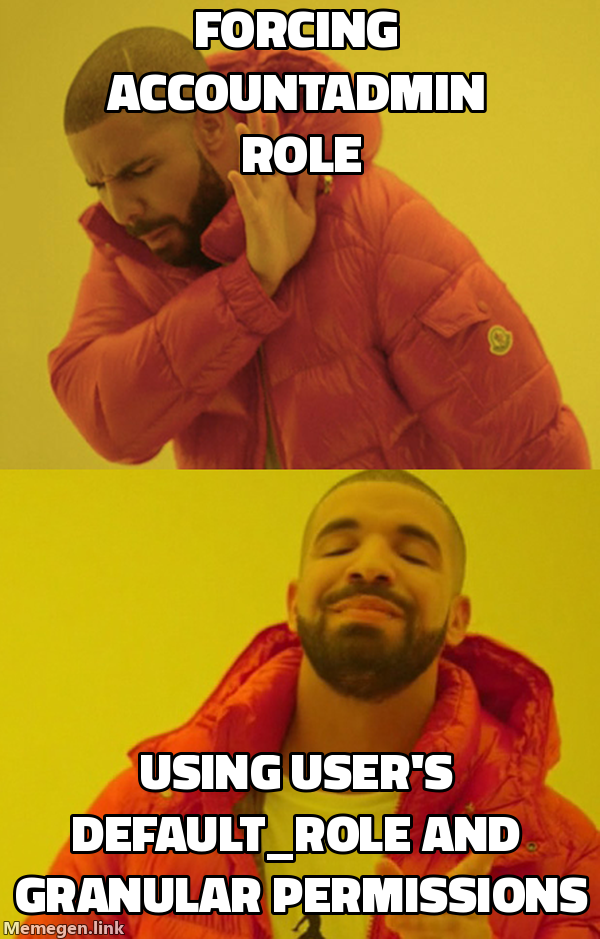
We've updated the Snowflake connector to stop forcing the ACCOUNTADMIN role, allowing it to correctly respect a user's DEFAULT_ROLE. Additionally, we overhauled SnowflakePermissionError messaging to recommend specific, least-privilege database roles (like USAGE_VIEWER or GOVERNANCE_VIEWER) instead of suggesting blanket IMPORTED PRIVILEGES. This improves security posture and makes troubleshooting permission issues much more intuitive.